Things I build to make offensive work faster. More shipping soon.
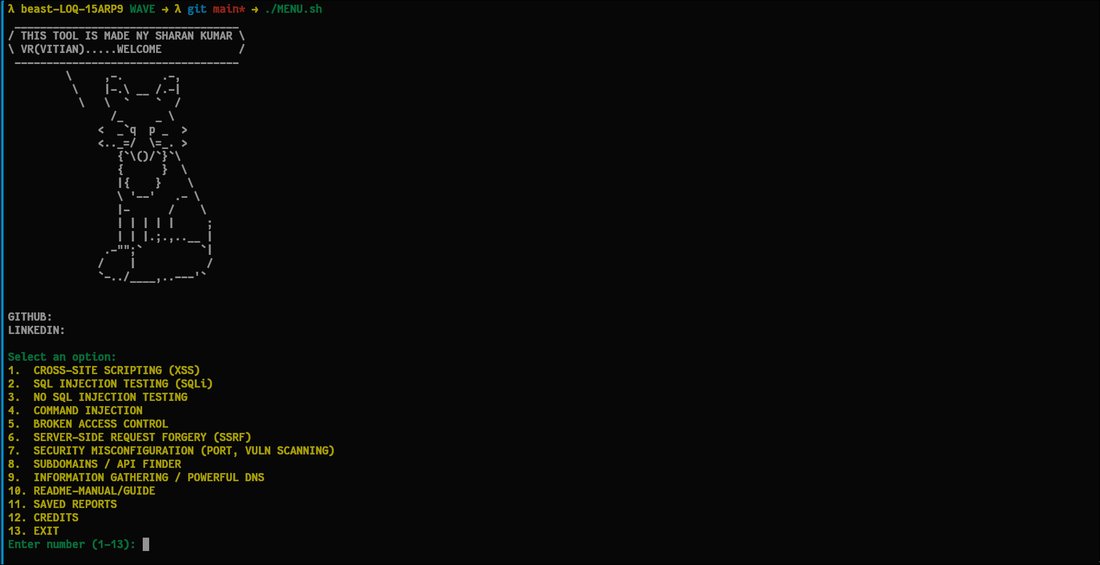
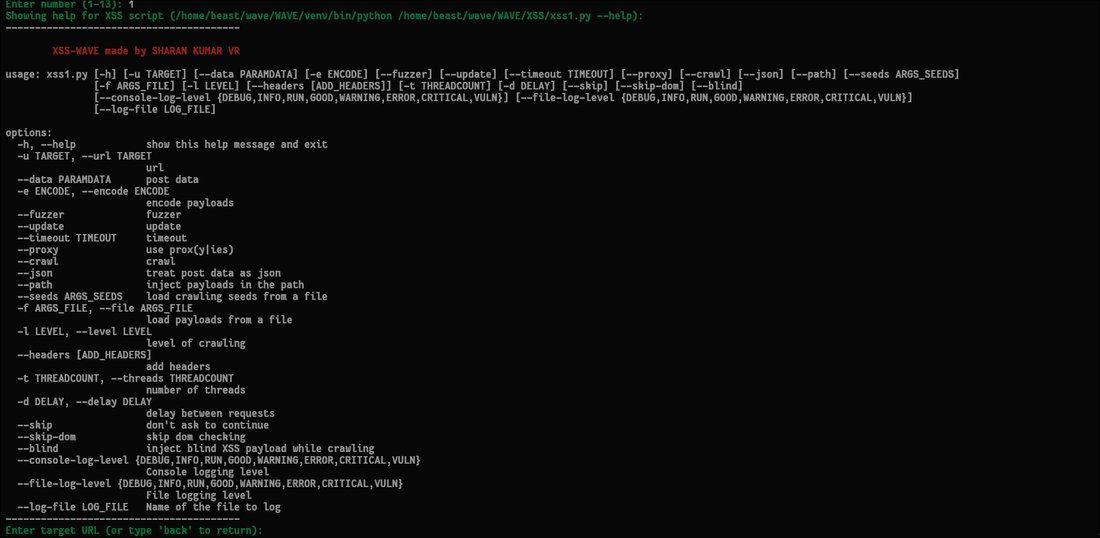
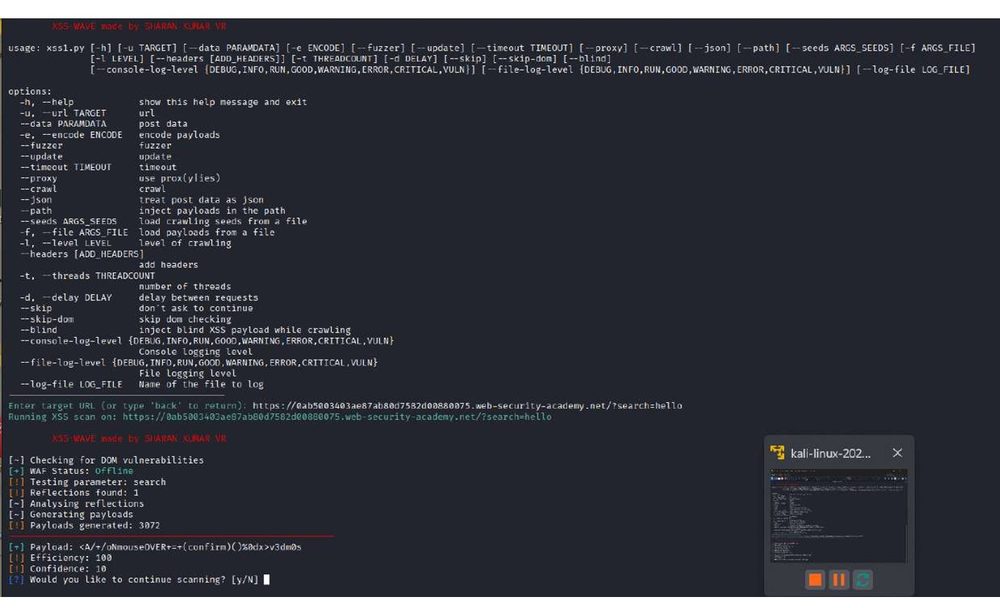
WAVE — automated web recon
One CLI for XSS, SQLi, SSRF, access-control, subdomain and API discovery, with reporting built in.
WAVE turns repetitive security checks into a streamlined CLI workflow — helping security researchers identify potential vulnerabilities faster, validate findings, and generate structured reports for analysis and documentation. Built with practical security testing and authorized assessment workflows in mind.
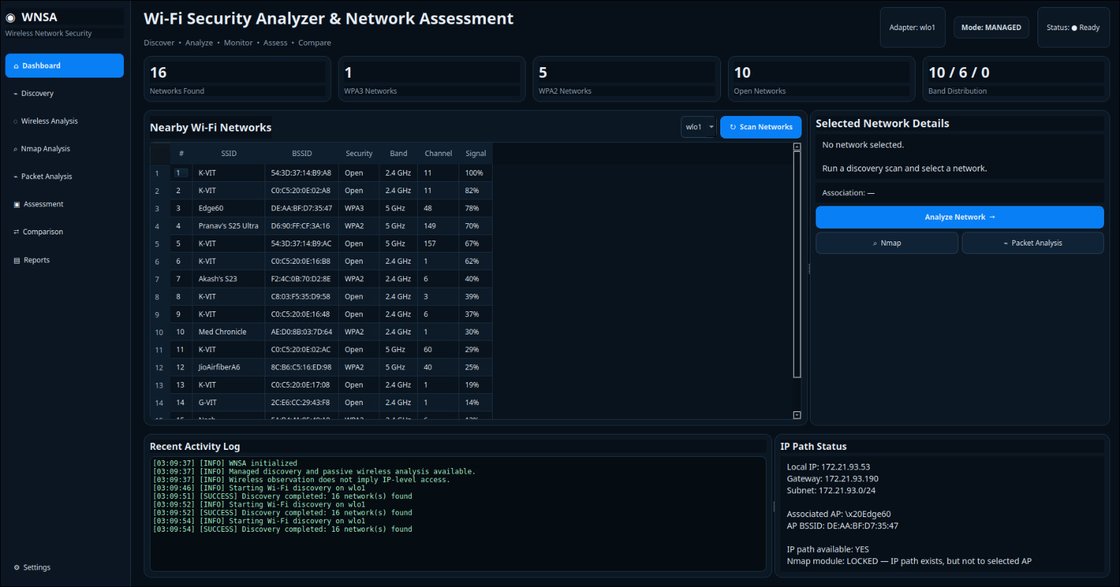
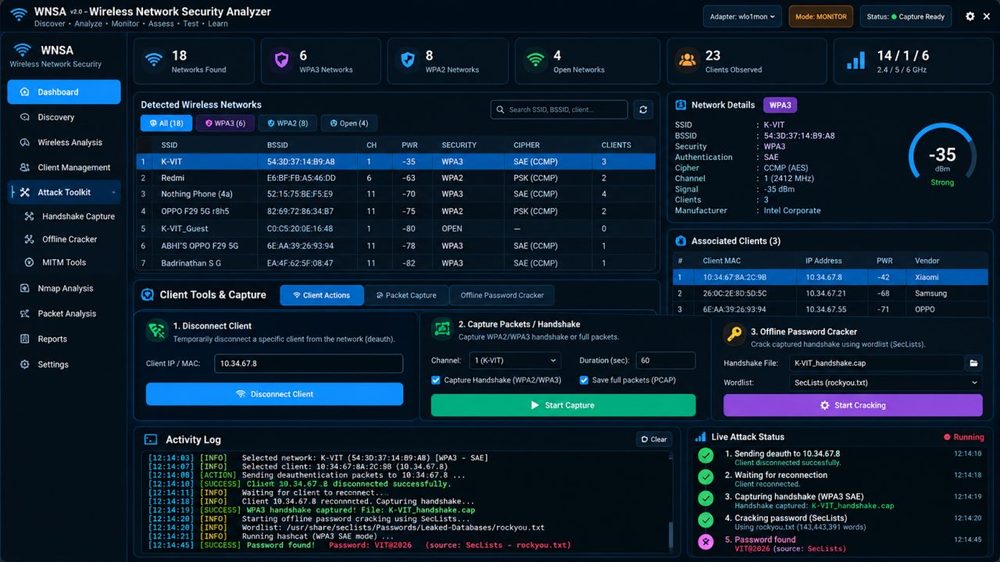
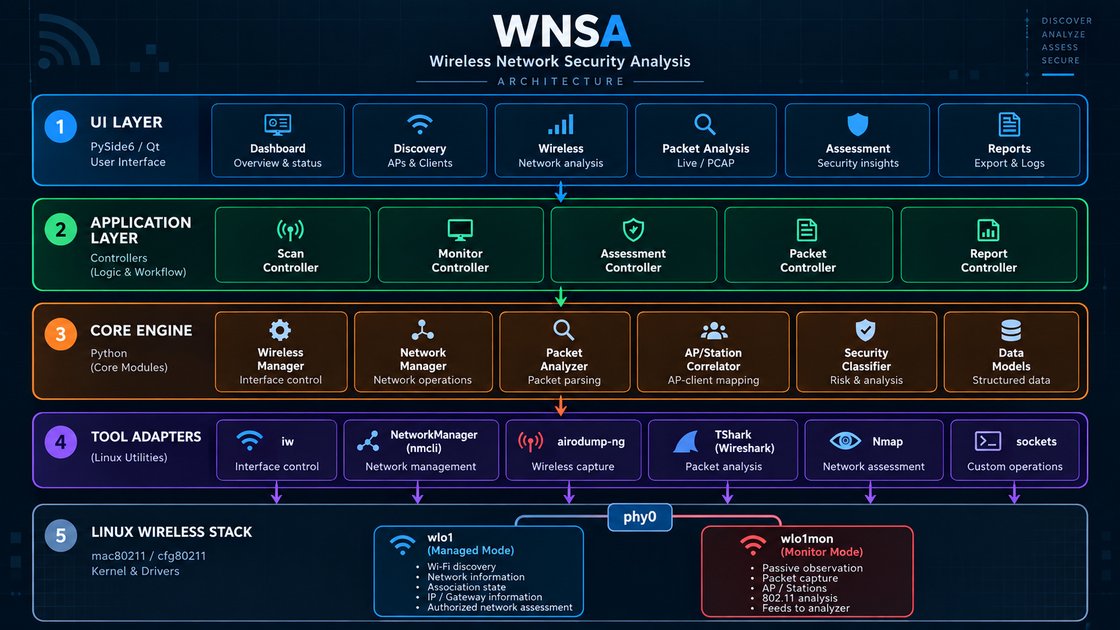
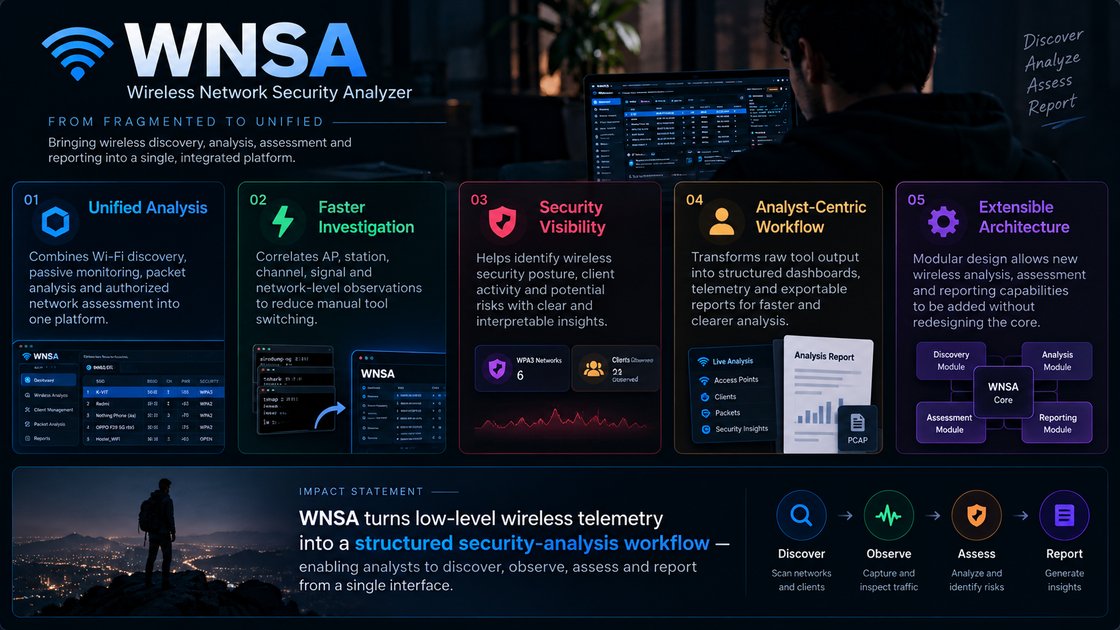
WNSA — wireless security workbench
802.11 discovery, monitor-mode capture, and WPA2/WPA3 handshake assessment in a single operator interface.
WNSA turns low-level 802.11 telemetry into actionable security intelligence — unifying wireless discovery, passive monitoring, packet analysis and authorized assessment in one workflow. It cuts tool fragmentation and gives analysts a structured, real-time view for faster investigation and evidence-driven reporting.
NeuralOps — AI-assisted SOC
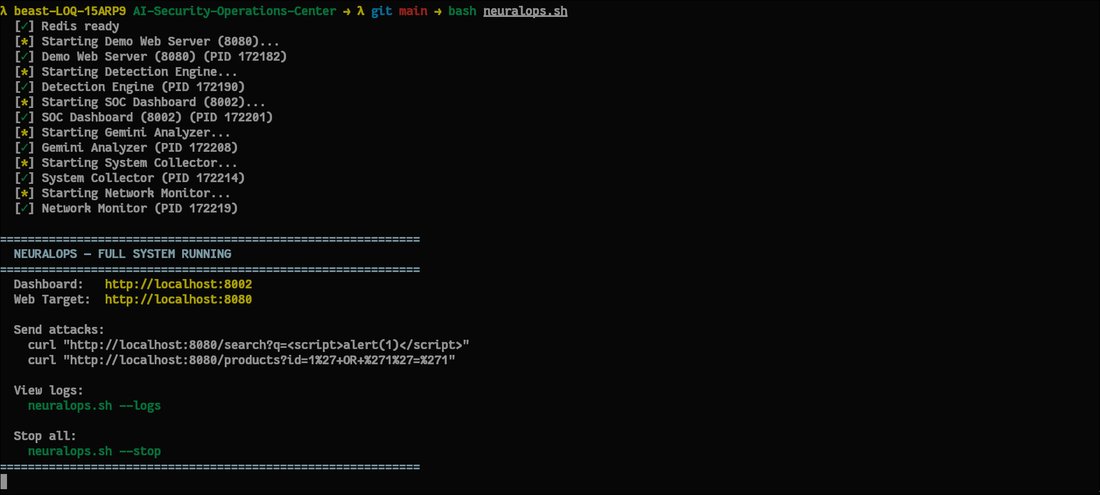
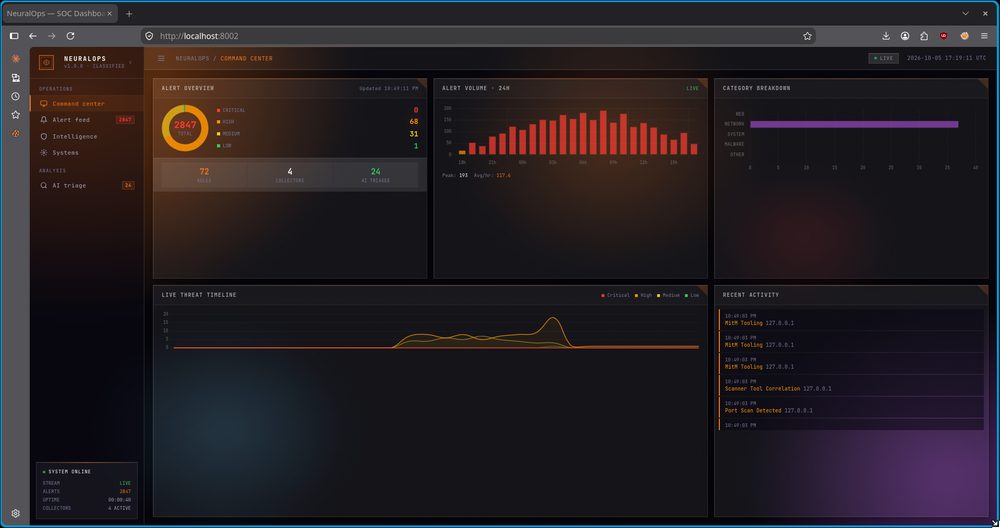
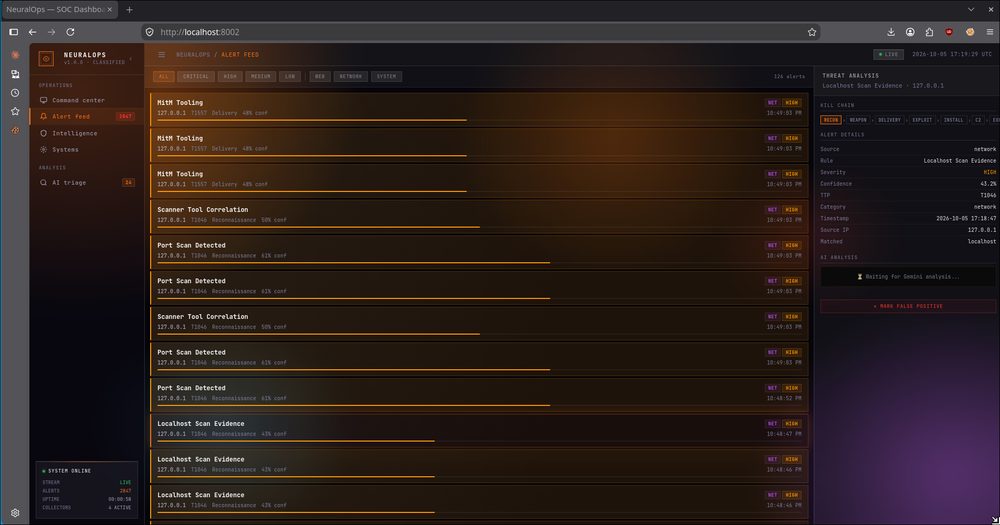
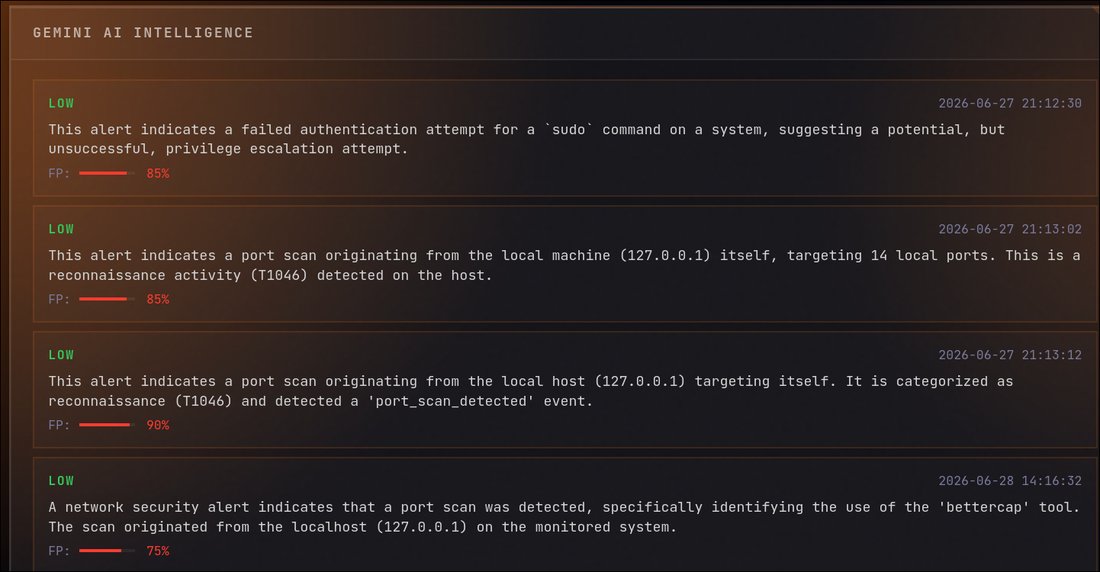
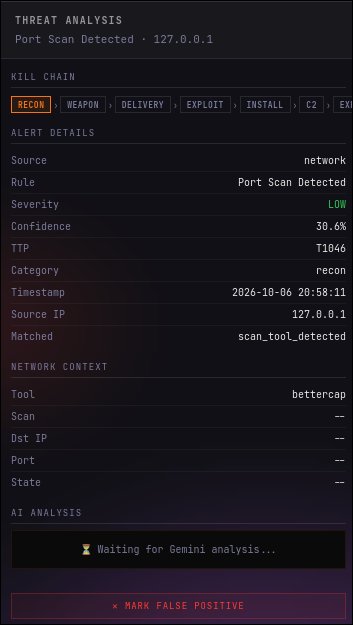
Live command center: alert volume, a threat timeline, and AI triage mapping activity to MITRE ATT&CK in real time — plus a full alert feed where every event is scored, classified, and given kill-chain context.
NeuralOps turns raw security events into a triaged, explainable stream — using an AI analyst to score alerts, map them to MITRE ATT&CK and surface what matters, so investigation starts from context instead of noise.
Echo Defend — security-ops automation
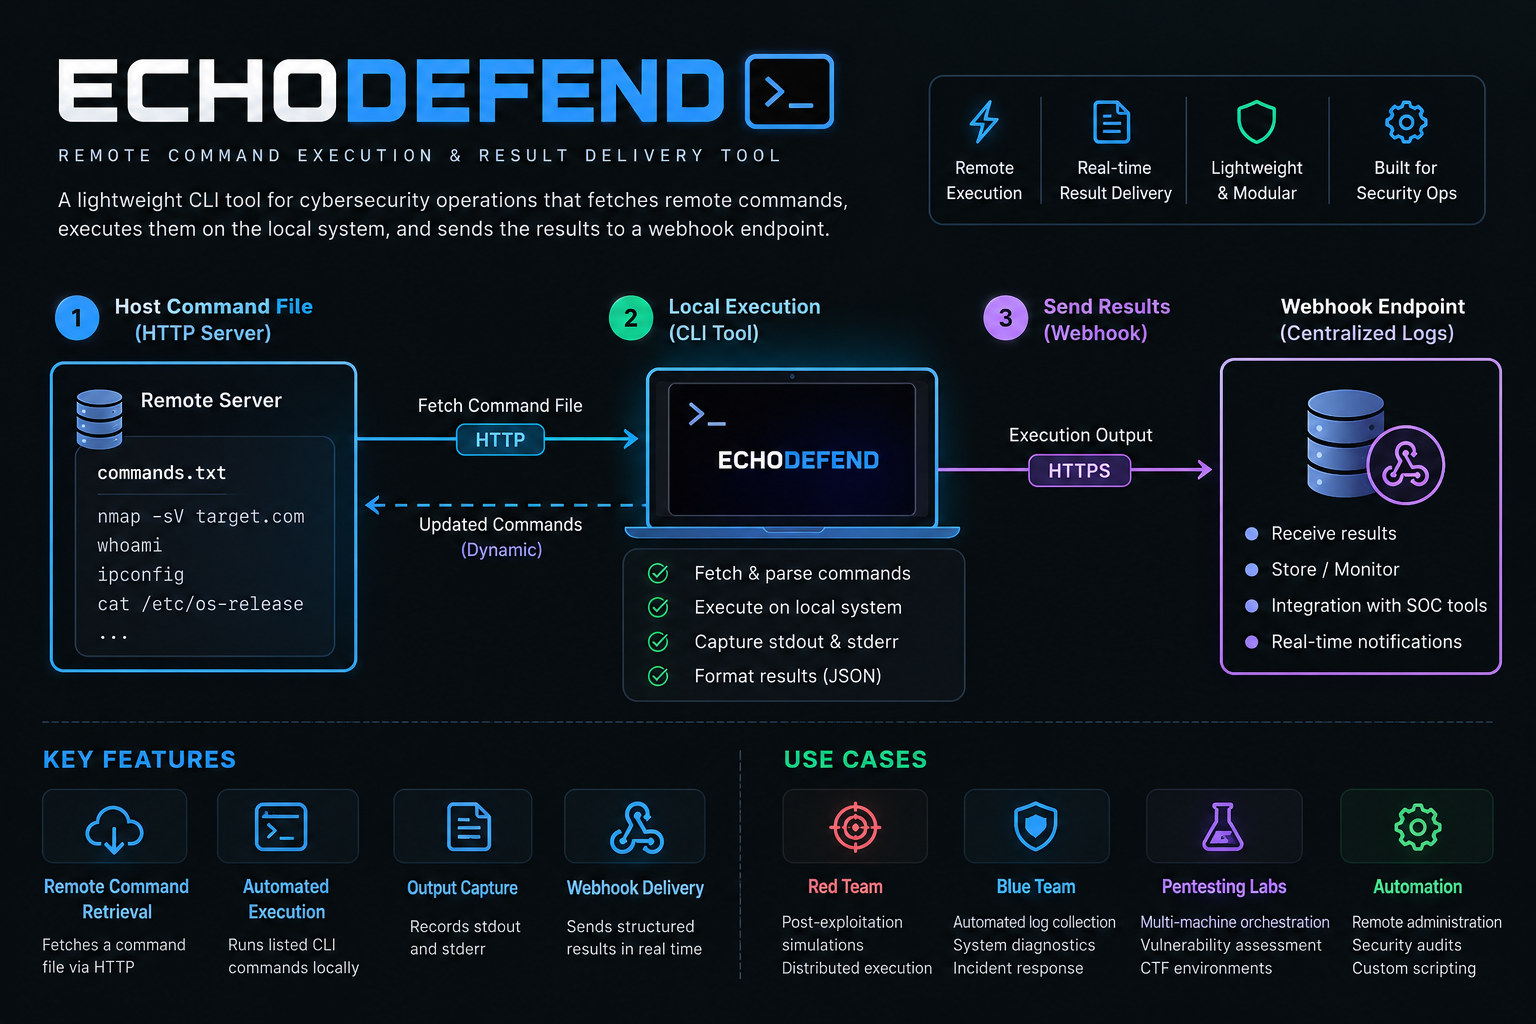
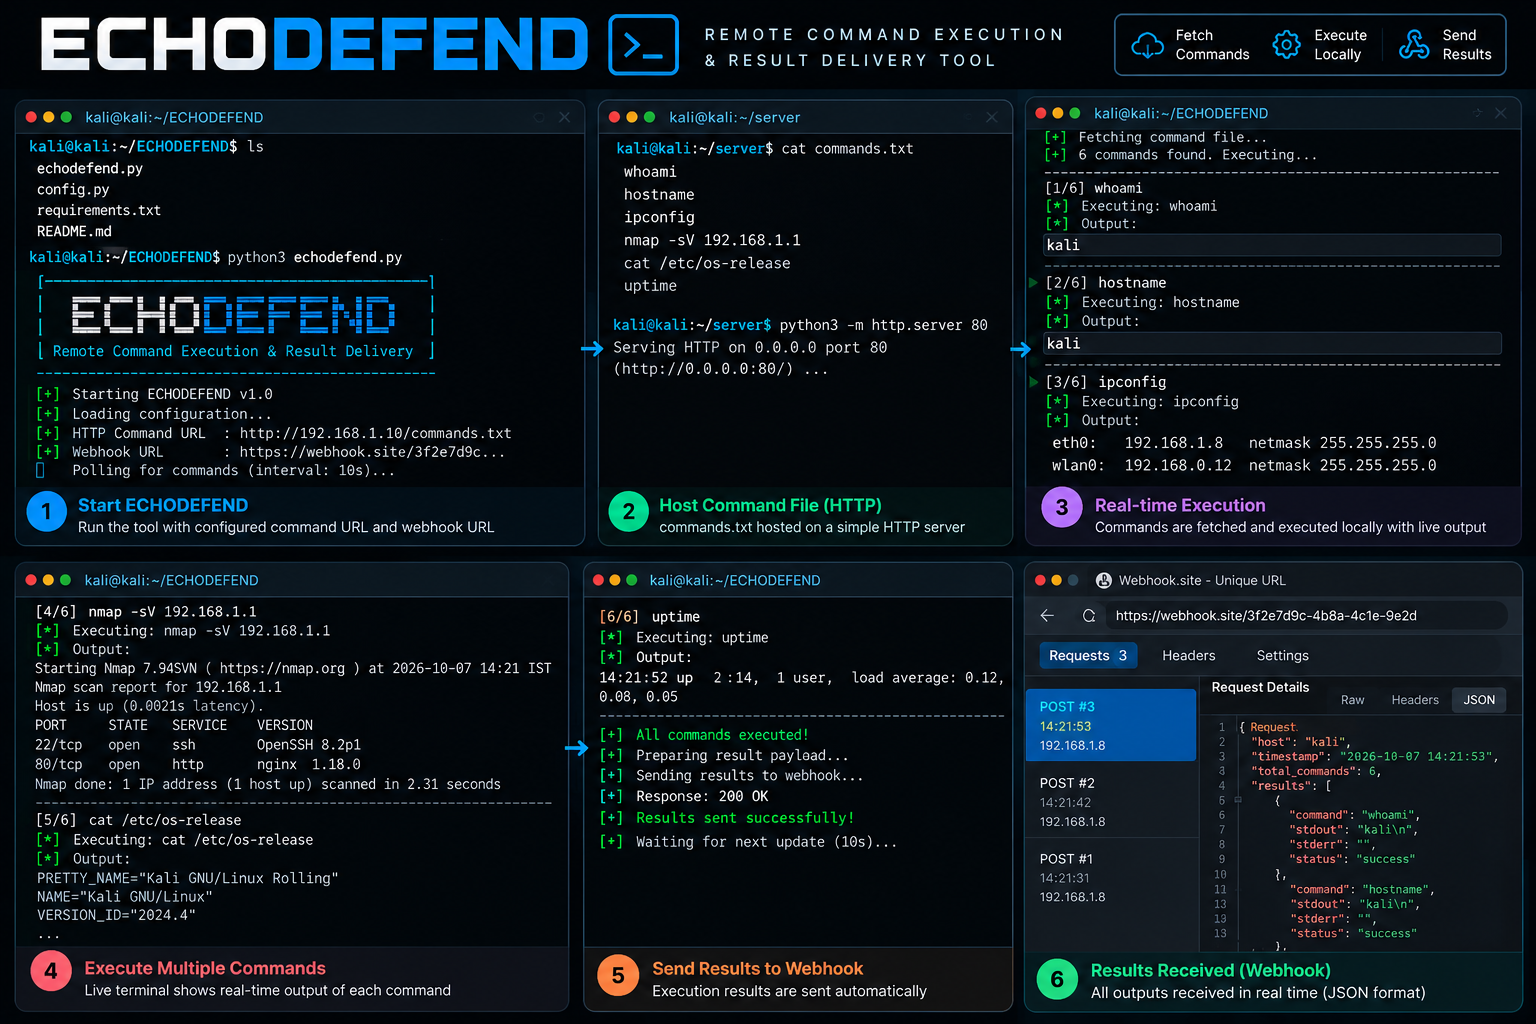
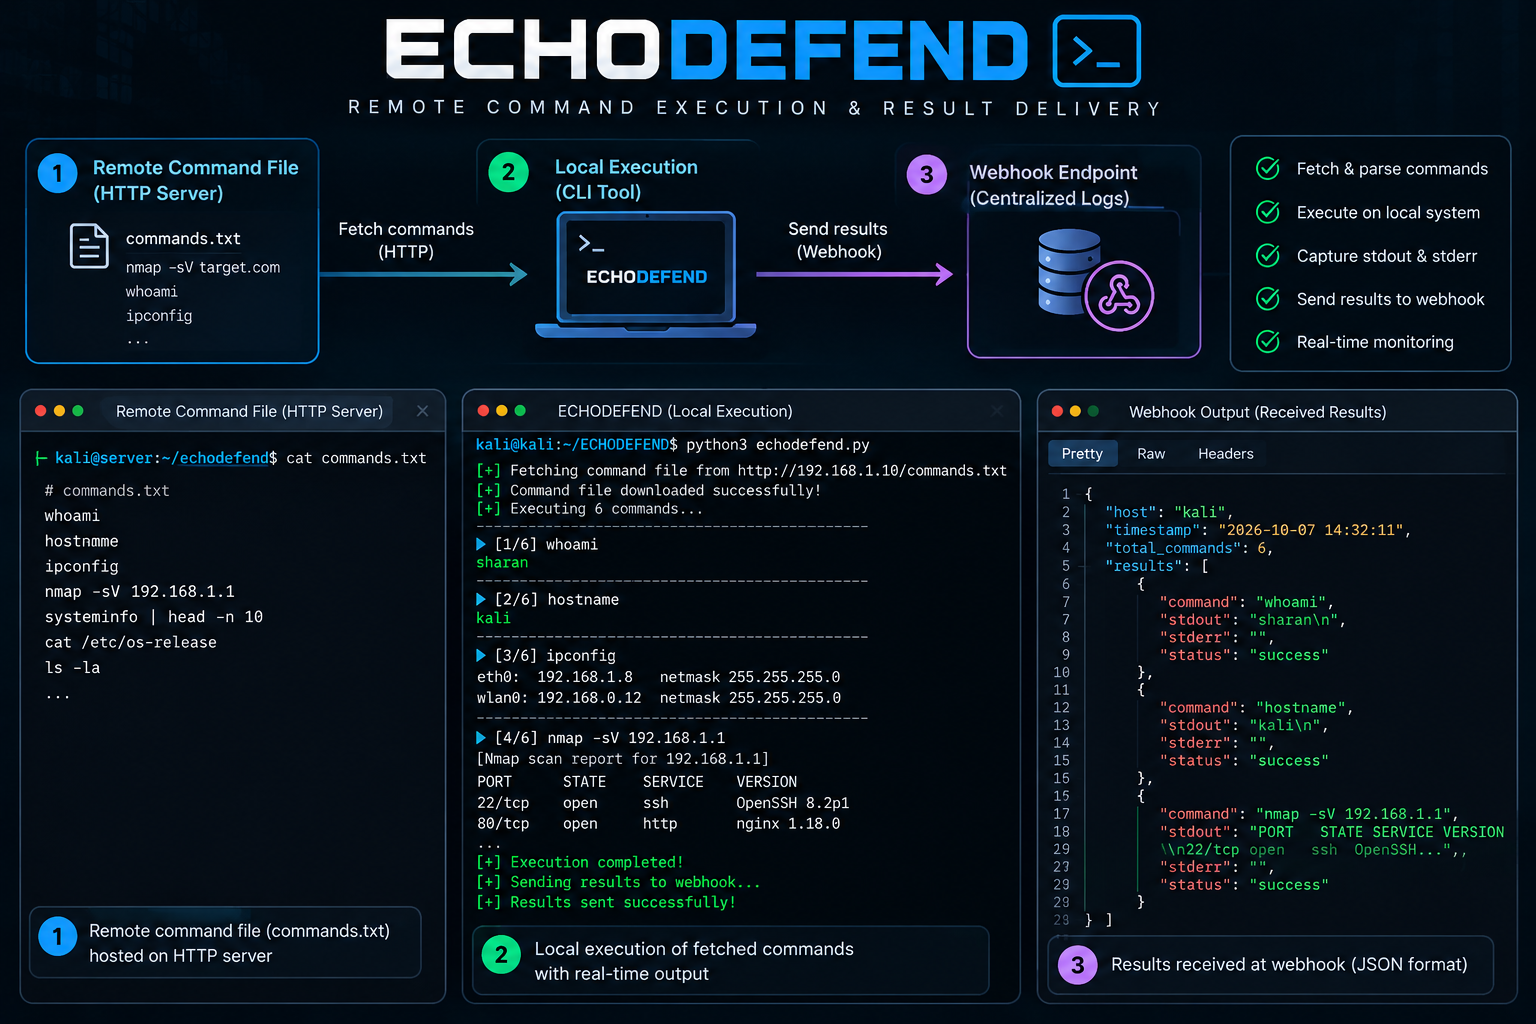
This one jumped straight out of my day-to-day lab — a script I wrote to take the repetitive parts of security ops off my hands (authorized command retrieval, local CLI execution, result capture and webhook delivery) that grew into a lightweight pipeline for controlled, authorized environments.
Echo Defend automates the repetitive parts of security operations — authorized command retrieval, local execution, result capture and delivery — so controlled, authorized workflows run hands-off and consistently.